Digital security remains a key topic in 2025. During the second quarter, thousands of new vulnerabilities were recorded that affected operating systems, applications and devices. This article summarizes the most important findings, with updated data and practical advice on how to protect yourself.
What are vulnerabilities and exploits?
Vulnerabilities are flaws in software that can be taken advantage of by attackers. When they are exploited, they make it possible to access systems, steal information or cause damage. Exploits are tools that take advantage of those flaws in order to carry out malicious actions.
Rise in vulnerabilities in 2025
More flaws every month
During the first six months of 2025, there was a steady increase in the number of vulnerabilities. In January, the figure exceeded 4,000, far higher than in previous years. This growth reflects both technological progress and the interest attackers have in finding new weaknesses.
Critical vulnerabilities on the rise
Vulnerabilities rated critical (CVSS > 8.9) also grew. Although not all of them receive this rating, many have detailed descriptions that help improve software security.
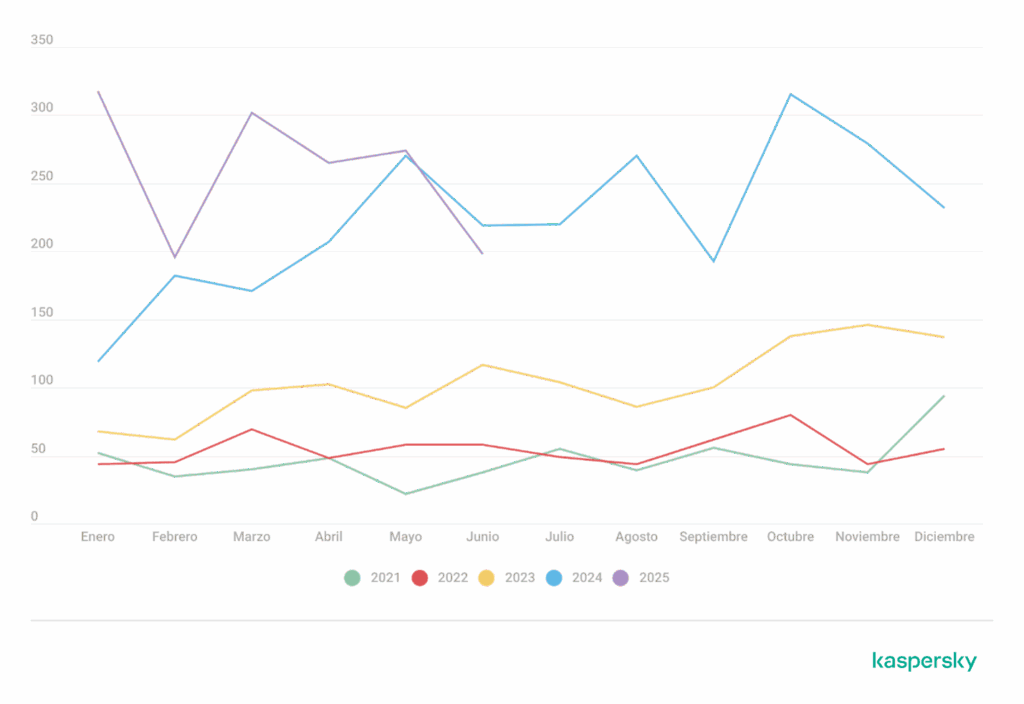
Total number of critical vulnerabilities published each month, 2021–2025
Main exploited vulnerabilities
Windows under attack
Microsoft Office products were the most attacked. The most widely used vulnerabilities were:
- CVE-2018-0802: allows code to be executed remotely.
- CVE-2017-11882: affects the Equation Editor.
- CVE-2017-0199: allows an attacker to take control of the system.
Attacks on WinRAR and on the Windows indexing system were also detected, with the goal of stealing credentials.
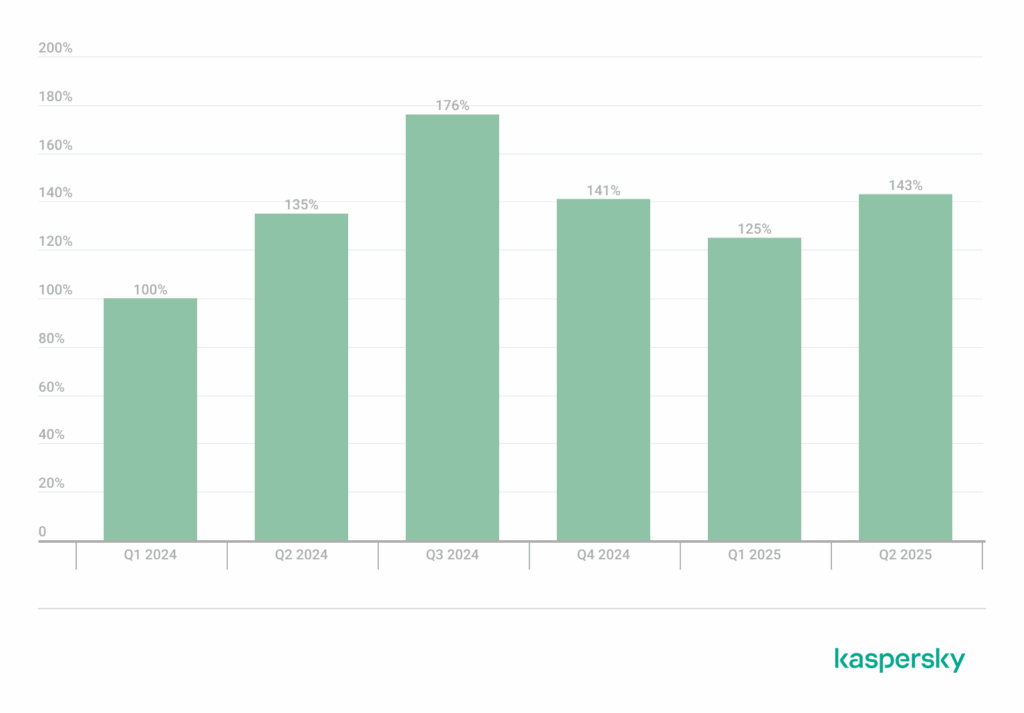
Percentage of Windows users affected by exploits between the first quarter of 2024 and the second quarter of 2025, using 100% in the first quarter of 2024 as the reference.
Linux is vulnerable too
Linux was not far behind. The most exploited flaws were:
- Dirty Pipe (CVE-2022-0847): allows privilege escalation.
- CVE-2019-13272: manipulates inherited privileges.
- CVE-2021-22555: affects the Netfilter kernel.
These attacks show that Linux is in the sights of criminals, especially because of its growing use in devices.
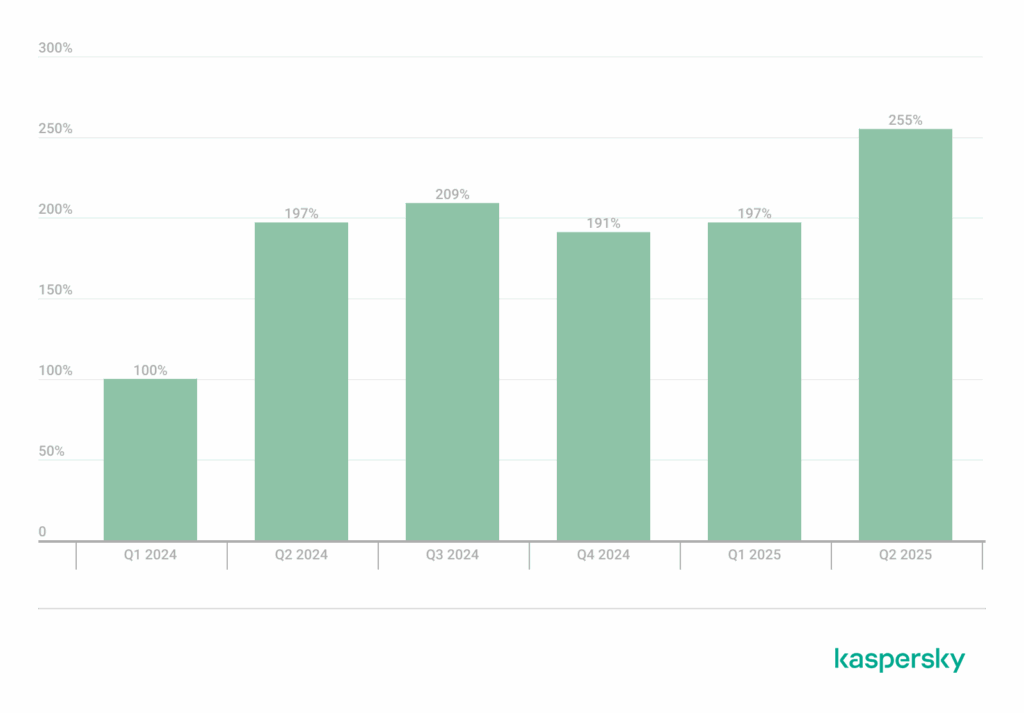
Percentage of Linux users affected by exploits between the first quarter of 2024 and the second quarter of 2025, using 100% in the first quarter of 2024 as the reference.
Most widespread exploits
Operating systems in the crosshairs
Exploits for operating systems were the most common. Although no new attacks against Microsoft Office were published this quarter, Windows and Linux systems remain the main targets.
APT attacks and key vulnerabilities
What are APT attacks?
APT attacks (Advanced Persistent Threats) are carried out by organized groups. They seek prolonged access to systems in order to steal information or cause damage.
The 10 most used vulnerabilities
Among those most exploited by APT groups are:
- CVE-2025-31324: affects SAP NetWeaver.
- CVE-2024-1709: critical vulnerability in ConnectWise.
- CVE-2024-31839 and CVE-2024-30850: flaws in the CHAOS tool.
- CVE-2025-33053: allows code to be executed in Windows.
These vulnerabilities were used to gain initial access and to control systems.
C2 frameworks in real attacks
What are C2 frameworks?
They are tools that let attackers keep control over compromised systems. The most used in 2025 were:
- Sliver
- Metasploit
- Havoc
- Brute Ratel C4
Some allow commands to be run, others require additional configuration. Attackers customize them to avoid being detected.
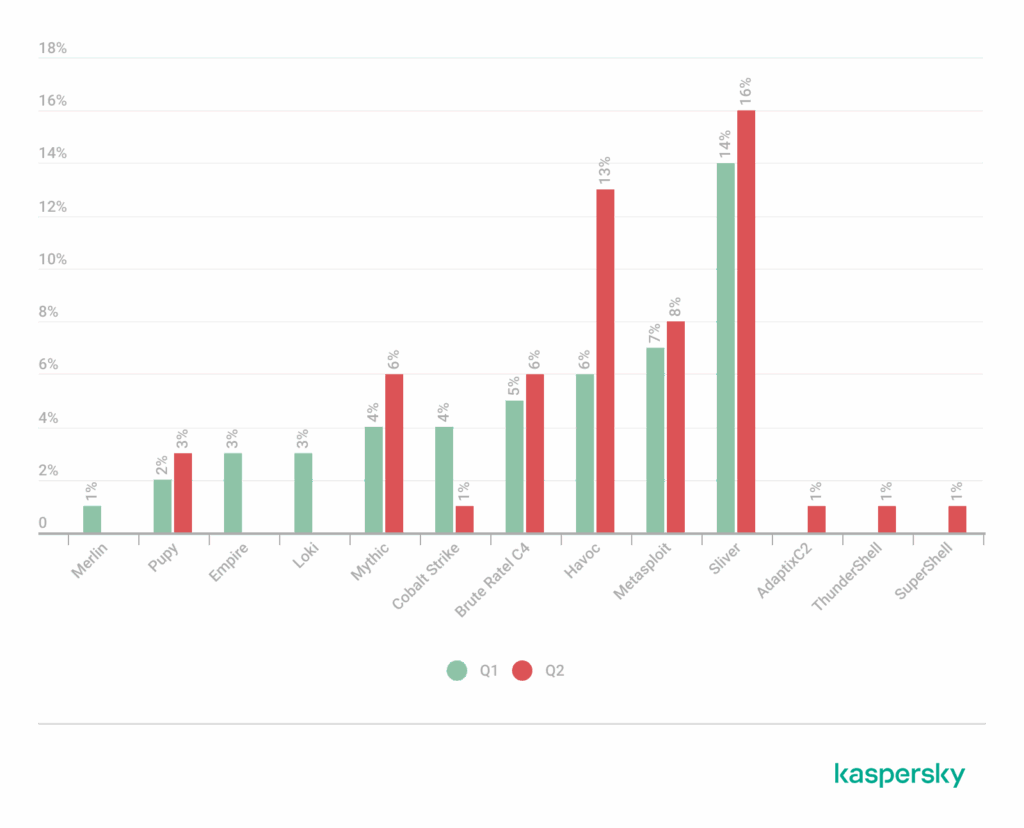
Ranking of the 13 C2 frameworks most used by APT groups in attacks during the first half of 2025
Notable vulnerabilities of the quarter
Flaws that drew attention
Among the most interesting vulnerabilities are:
- CVE-2025-32433: allows commands to be run on SSH servers without authentication.
- CVE-2025-6218: directory traversal in WinRAR.
- CVE-2025-3052: insecure data access in UEFI.
- CVE-2025-49113: insecure deserialization in Roundcube Webmail.
- CVE-2025-1533: stack overflow in the AsIO3.sys driver.
These flaws show how attackers take advantage of simple errors to compromise systems.
Recommendations for protecting yourself
Constant updates
Installing security patches is key. Updates fix known flaws and keep exploits from working.
System monitoring
It is important to watch how devices behave. Detecting suspicious activity in time can prevent greater damage.
Workstation protection
Using reliable solutions to block malicious software is essential. Tools such as Kaspersky Next offer comprehensive protection for companies of every size.
The second quarter of 2025 made it clear that digital security must be a priority. With thousands of new vulnerabilities and increasingly sophisticated attacks, protecting systems is more important than ever. Updating software, monitoring devices and using security tools are fundamental steps to stay safe.